1 min read
Double Your Coins Today: Don’t Fall for a Crypto Scam
What are Crypto Scams? Crypto scams are a type of investment fraud where criminals use the mechanics and mystique of cryptocurrency to deceive...
8 min read
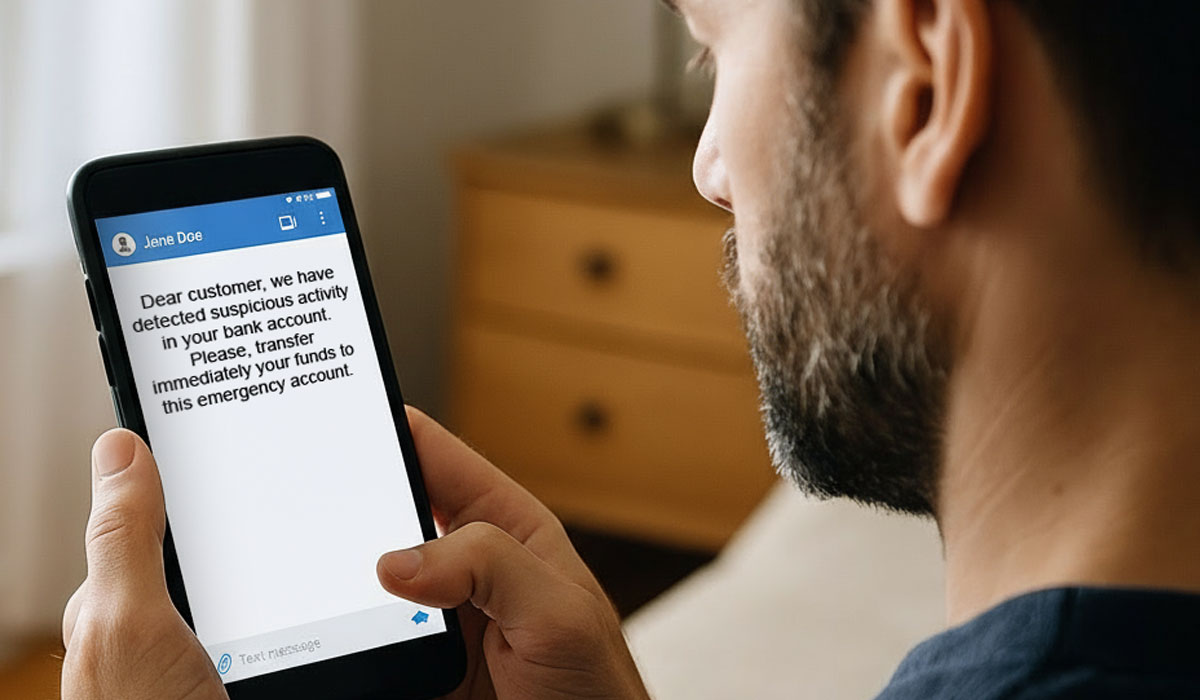
Impersonation fraud, the "safe account scam" where criminals pose as a bank, the police, or another trusted organisation to move funds, is actually one of the few APP fraud categories moving in the right direction.
UK Finance's Annual Fraud Report 2026 shows losses from impersonation and related "malicious redirection" scams fell 12% in 2025, continuing a multi-year decline from over half of all UK APP fraud losses in 2020 to under a quarter today. That's a genuine sign that layered controls, payee verification, callback checks, and in-app warnings are working. It isn't a sign the threat has gone away: fraudsters are simply having to work harder, which is exactly why the tactics in this article (AI voice cloning, reverse-proxy MFA relay, rapid mule routing) keep evolving.
Although bank impersonation scams vary depending on the fraudster's pretext, most follow the same four-stage attack lifecycle.
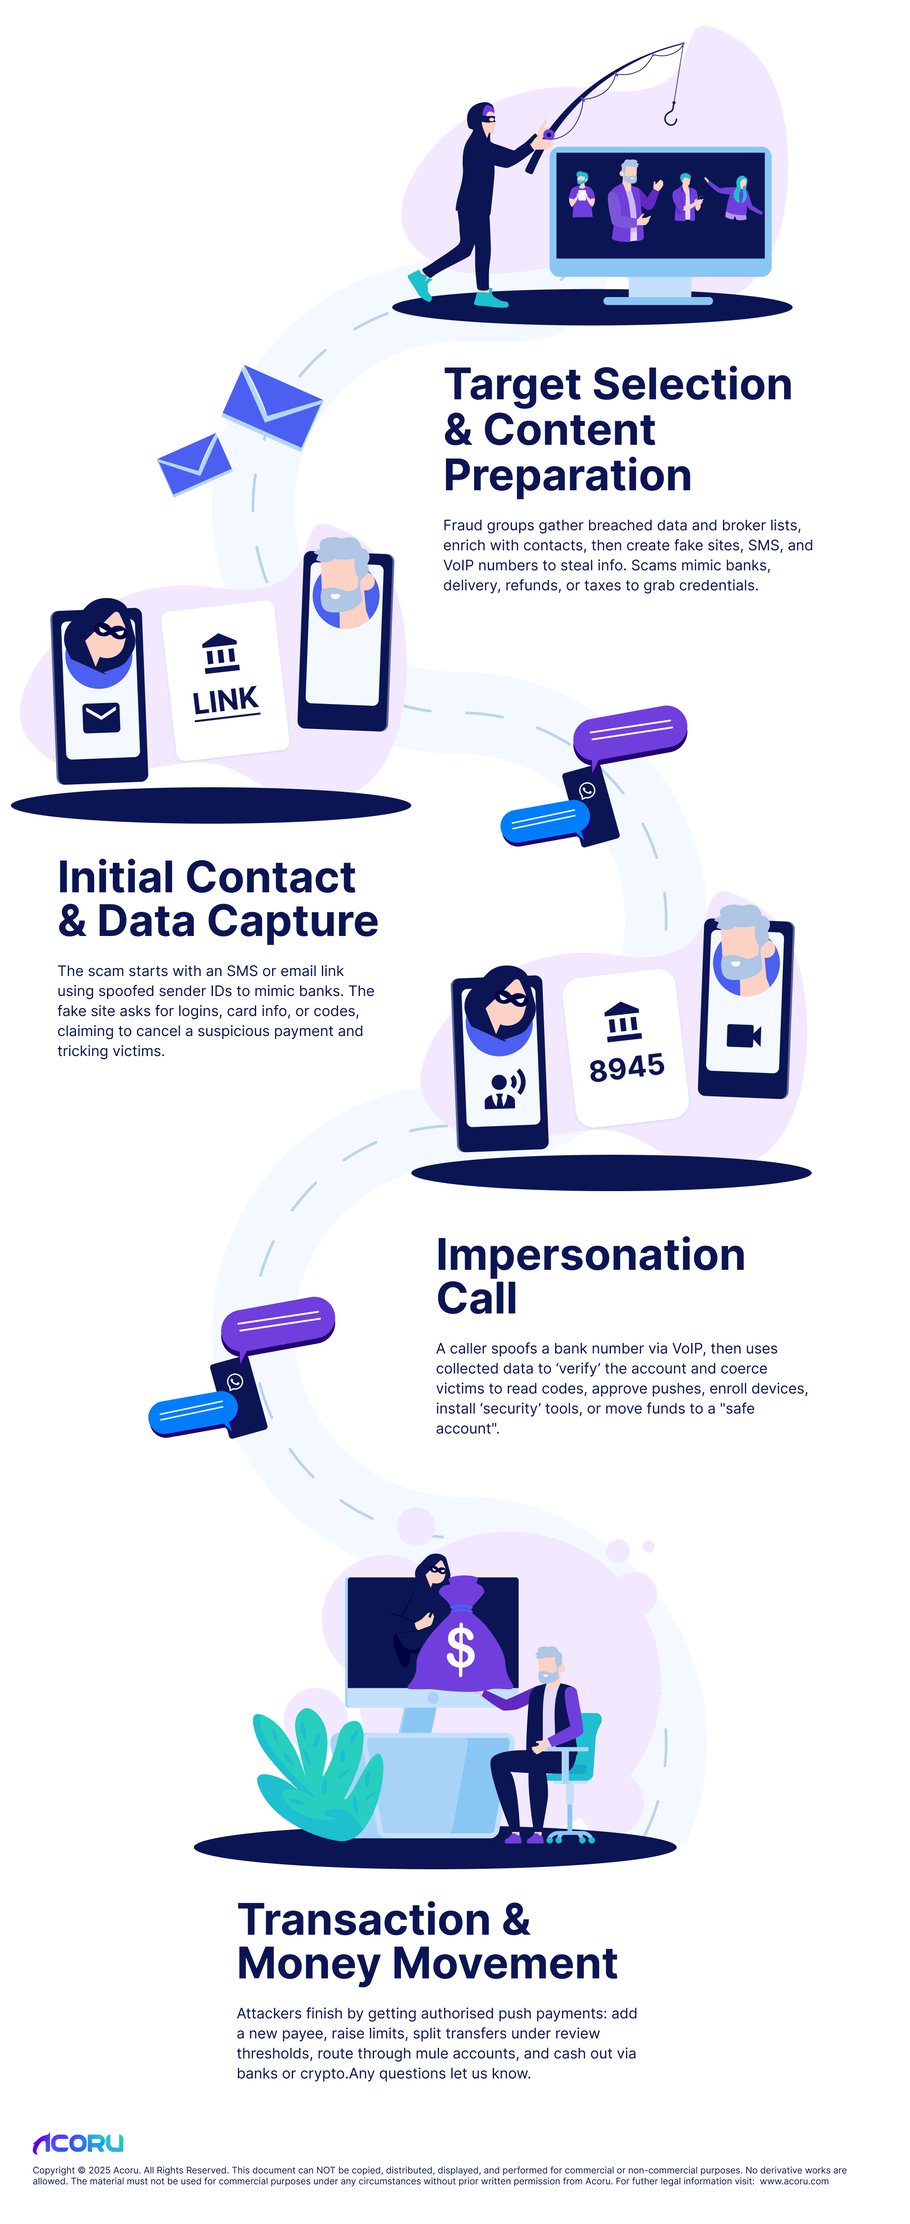
Fraud groups assemble target lists from breached datasets, lead brokers, and recycling of older phishing logs, then enrich with phone numbers, email addresses, and bank brands. In parallel, they build the pretext and infrastructure: a short SMS script, a look-alike website (often with valid TLS and cloned UI), and local VoIP numbers that match the victim’s region.
Pretexts aren’t only “bank” pages. Parcel delivery, retailer refunds, investment portals, and tax notices are common on-ramps designed to harvest credentials, one-time codes, device info, and personal details that will stand up in later “verification” steps.
The initial contact is usually an SMS or email containing a link to a lure site. Texts often use sender-ID spoofing so messages appear in the existing thread titled with the bank’s name on the handset. The fake website requests logins, DOB/postcode, card fragments, or prompts for codes under the guise of “cancelling a suspicious payment.”
A live caller phones from a number that appears to be the bank (cheap to do with VoIP caller-ID spoofing, especially when calls originate outside jurisdictions enforcing strict attestation). Increasingly, fraudsters also use AI voice cloning to make these calls sound even more convincing. Using data already collected, the caller “verifies” the account, then steers the victim through actions the attacker needs: reading back a code, approving a login/push, enrolling a “secure device,” installing a “security tool,” or moving funds to a “safe account.”
With control of the session (and the narrative), attackers usually finish by executing authorised push payments. They get victims to add a new payee, raise limits, and send funds. Payments are split to stay below review thresholds and routed through money mule networks, then cashed out, forwarded across banks, or converted via crypto on-ramps.
| Category | Score (/10) | Key Insights | |
| 1 | Initial Investment Scammer Setup Cost |
 Moderate · 5/10 |
Bank-impersonation runs on readily available parts: leaked data, cheap domains with passable branding, SMS routes, and VoIP numbers. Kits for fake banking pages and scripted lures are widely sold and reused, so setup is mostly integration and rehearsal, not R&D. Costs rise when you add highly accurate voice cloning, better hosting hygiene, or mule onboarding. Still, it’s a mid-cost campaign to run, not something requiring high investment. |
| 2 | Exposure Risk Likelihood of Getting Caught |
|
Phone and SMS leave traces like caller records, message routes, takedown trails, and contact-center recordings. Money mules add another point of failure if they’re identified. That said, VoIP churn, cross-border routing, and quick cash-out keep personal exposure manageable. |
| 3 | Success Rate Likelihood of Scamming a Victim | Moderate · 6/10 |
The scam hinges on timing and persuasion: catching customers during real activity, sounding credible, and driving a few critical steps (new payee, limit change, high-value transfer). Education, name-check warnings, and in-app approvals blunt many attempts, yet multi-stage pretexts still convert often enough, especially off-hours, with first-time payees, or when a live caller manages the script. |
| 4 | Return on Investment ROI |  Moderate to High · 9/10 |
When a bank impersonation scam lands, payout is strong. Authorized push payments clear quickly, and reversals are hard. Infrastructure is reusable across brands and regions, and harvested data fuels further fraud long after the first hit. With instant rails, funds move before scrutiny catches up. |
Rather than educating customers with notices on the bank’s website, move the awareness closer to the point of highest risk. Include short plain-language messages in the mobile app during risky actions (adding a payee, raising limits, like “We will never ask for your OTP or to move funds to a ‘safe account’.”
Even when a scam is months in the making, the payoff hinges on a few actions that must succeed in a short window. Brief holds and extra checks at those moments make the attack less reliable and more visible. This can include things like short waiting periods for the first payment to a new payee (show a countdown and status), lower daily caps for first-time payees and recently changed limits, name-mismatch warnings on payees that require an explicit “proceed anyway, or second approver or scheduled callback for large or overseas transfers.
Caller ID, texts, and emails are easy to spoof. If the impostor controls the conversation there, they can walk a customer through any “security step.” Pulling the decision back into a trusted channel breaks that control. In-app messaging and bank-initiated callbacks (requested inside the app) for certain actions can work here.
These scams unfold across multiple stages. A text today, a fake website tomorrow, a call next week, followed by a new payee and a transfer. Each step can look routine in isolation, but together they signify a scam in motion. Acoru’s fraud detection solution identifies risk using pre-fraud signals across all channels, before a fraudulent transaction takes place.
Financial institutions should treat bank impersonation scams as a multi-stage attack and move detection upstream to the pre-fraud stages.
This is also one of the clearest cases where regulation and detection point the same direction. The UK's Confirmation of Payee scheme and the EU's Verification of Payee mandate (in force for euro-area sending institutions since October 2025) both exist specifically to catch the moment a customer is directed to a name-mismatched "safe account." A payee-name mismatch is a strong signal in isolation; correlated with the SMS, spoofed call, and OTP-relay activity that typically precede it, it's close to a confirmed attack in progress.
That means watching for pre-fraud signals: indicators that something nefarious is underway. These signals can include look-alike domains tied to the bank's brand, proxy fingerprints, OTP relay behaviour, customer credential exposure, confirmation-of-payee mismatches, and sudden contact-detail changes.
None of these signals alone proves fraud. Together, they reveal an attack as it develops. Financial institutions ultimately need pre-fraud signal intelligence to be able to take action early enough to interrupt bank impersonation scams before a transaction is initiated.
Also, checks like caller ID, SMS OTP, and knowledge-based prompts no longer signal safety when fraudsters can easily control the conversation and the context. The anchor of trust may need to shift away from customers’ phone networks and toward bank-controlled channels.
Bank impersonation scams affect financial institutions and customers worldwide. The following real-world examples from across Europe illustrate how these attacks are carried out and the financial impact they can have.
In March 2025, elEconomista reported on the arrest of a 24-year-old who defrauded victims out of more than €200,000 by posing as a bank security employee. The report describes how the fraudster used prior info obtained about the victims to make the later stages of the scam easier to fall for. These later stages involved phone calls and text messages posing as a bank employee and requesting the victims take certain actions that transferred money to accounts under his control.
A South London man received a jail sentence of five years after defrauding bank customers of £988,719 (over €1 million) through bank impersonation. In a classic case of the multi-channel nature of these scams, the perpetrator first called victims, pretending to be investigating fraudulent activity. Then, victims would get directed to a fake website, where they’d unknowingly disclose their important account details. The fraudster then used those details to transfer funds to mule accounts under his control.
In 2025, a French court ordered BNP Paribas to reimburse a customer who had previously fallen victim to a bank impersonation scam. This particular scam exploited the trust relationship between the customer and his bank advisor at BNP Paribas. The fraudster was able to spoof his telephone number to appear as the customer’s usual bank advisor. The fake advisor directed the customer to transfer funds totalling €54,000.
In July 2025, the Bavarian Police in Germany issued a press release that described bank impersonation scams conning customers out of €100,000. The tactics rested on fraudulent phone calls posing as bank employees. In an interesting exploitation of real time payments using push-based approval, the fraudsters told victims they were hacked and that to confirm the return of funds to their accounts, they needed to approve push notifications on their banking apps. In fact, these push notifications ended up approving real-time transfers to the fraudsters’ accounts.
In a demonstration of the scale of these scams, Dutch police swooped in to arrest 8 people suspected of running a bank impersonation operation in September 2025. The eight scammers posed as bank helpdesk employees. Typically, they’d spoof their phone numbers to appear as the customers’ banks, inform customers of an account hack, and advise transfer to supposedly safe accounts. These accounts were in fact under the control of fraudsters. Up to 150 people lost a total of €1.6 million from this gang’s activities.
Generative AI will continue to strengthen fraudsters' capabilities by enabling natural-language scripts in any dialect, cloned voices that mimic trusted bank employees, and low-cost automation that coordinates SMS, phone calls, and fraudulent websites at scale.
The operating model needs to shift from “prove the loss after” to “see the setup before.” That means continuous account classification across the lifecycle (onboarding, device changes, contact-detail edits, beneficiary creation, outbound transfers). Also, those companies that best prevent these scams will need a pre-fraud signal intelligence fabric that links what’s happening across channels. This needs to be done through omnichannel orchestration that connects the dots across all channels.
See how Acoru helps financial institutions detect bank impersonation scams before fraudulent payments take place. Request a demo.
A bank impersonation scam is a type of authorised fraud in which criminals pose as a legitimate bank, by phone, text, email, or fake website, to trick customers into sharing credentials, approving a fraudulent transaction, or moving money to an account the fraudster controls.
A safe account scam is the most common form of bank impersonation: the fraudster tells the victim their account has been compromised and that funds must be urgently moved to a "safe account" for protection. The account is entirely controlled by the fraudster.
Using caller-ID spoofing and SMS sender-ID spoofing, criminals can make a call or text appear to come from a legitimate bank number, sometimes appearing in the same message thread as genuine bank alerts, making the contact look authentic even to cautious customers.
It's mixed. UK Finance's 2026 data shows losses from impersonation-style scams actually fell 12% in 2025, as banks have layered in stronger controls. But the underlying tactics, AI voice cloning, reverse-proxy MFA relay, rapid mule routing, continue to evolve, so the decline reflects better defences, not a disappearing threat.
No. Legitimate banks will never ask a customer to transfer funds to a different account, whether described as "safe," "protected," or otherwise, to resolve a security concern.
By correlating signals across channels rather than relying on any single check, look-alike domains, OTP-relay behaviour, sudden contact-detail changes, and payee-name mismatches individually look routine, but together they reveal an attack in progress well before the final transaction.
1 min read
What are Crypto Scams? Crypto scams are a type of investment fraud where criminals use the mechanics and mystique of cryptocurrency to deceive...
1 min read
How Emotional Manipulation Drives Mobile Scams "Hi Dad” scams, also known as “Hi Mum” scams, are a type of authorized fraud (scam). These scams...
1 min read
Authorized push payment (APP) fraud is a type of scam in which criminals manipulate victims over days or even weeks before convincing them to...